Skip to content

Vekri Control

One console to govern enterprise AI.

Vekri Control is where security teams see AI applications, endpoints and agents, configure detection and policy, simulate decisions, decide approvals and investigate activity, with every permission checked on the server.

  • Shared view for security and platform teams

    One place to answer: which AI, what access, what happened, who approved it.

  • Server-side authority

    The console holds no secrets and makes no decisions; the server authorizes and audits every request.

  • Self-hostable

    Runs in your Kubernetes cluster with the rest of Vekri, or in Vekri's cloud.

See it work

Vekri Control, step by step.
Vekri Control
Illustrative data
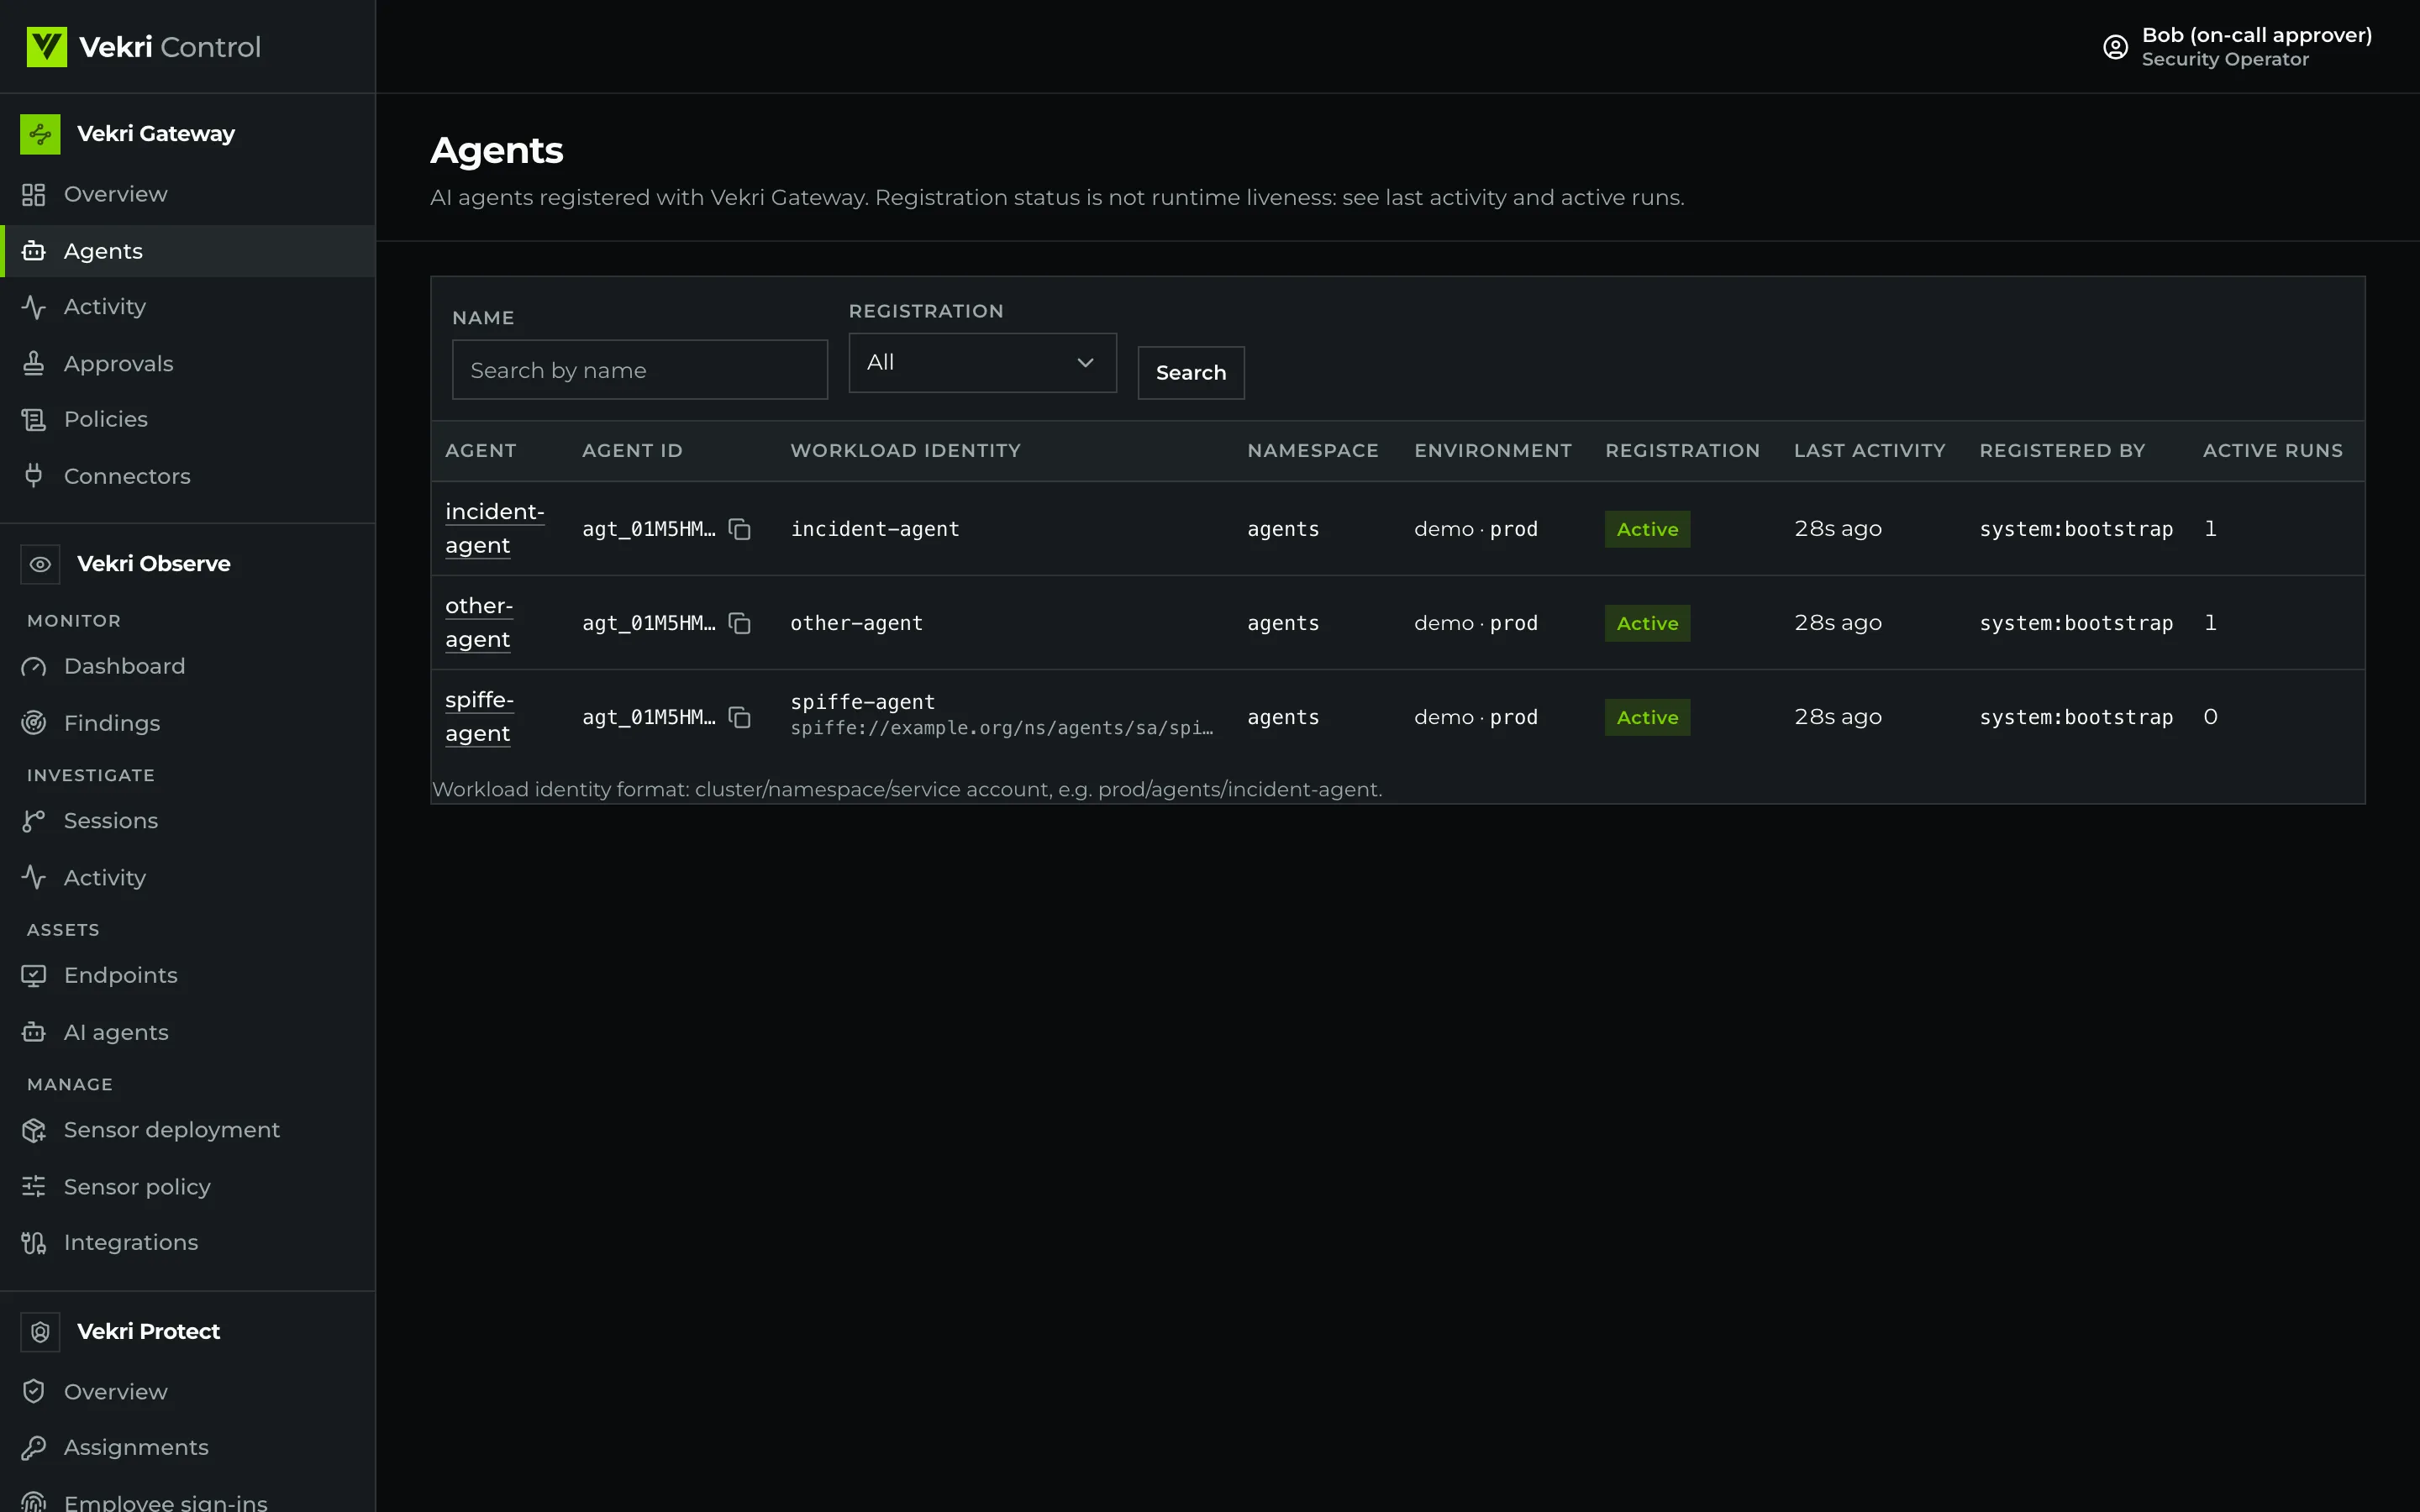
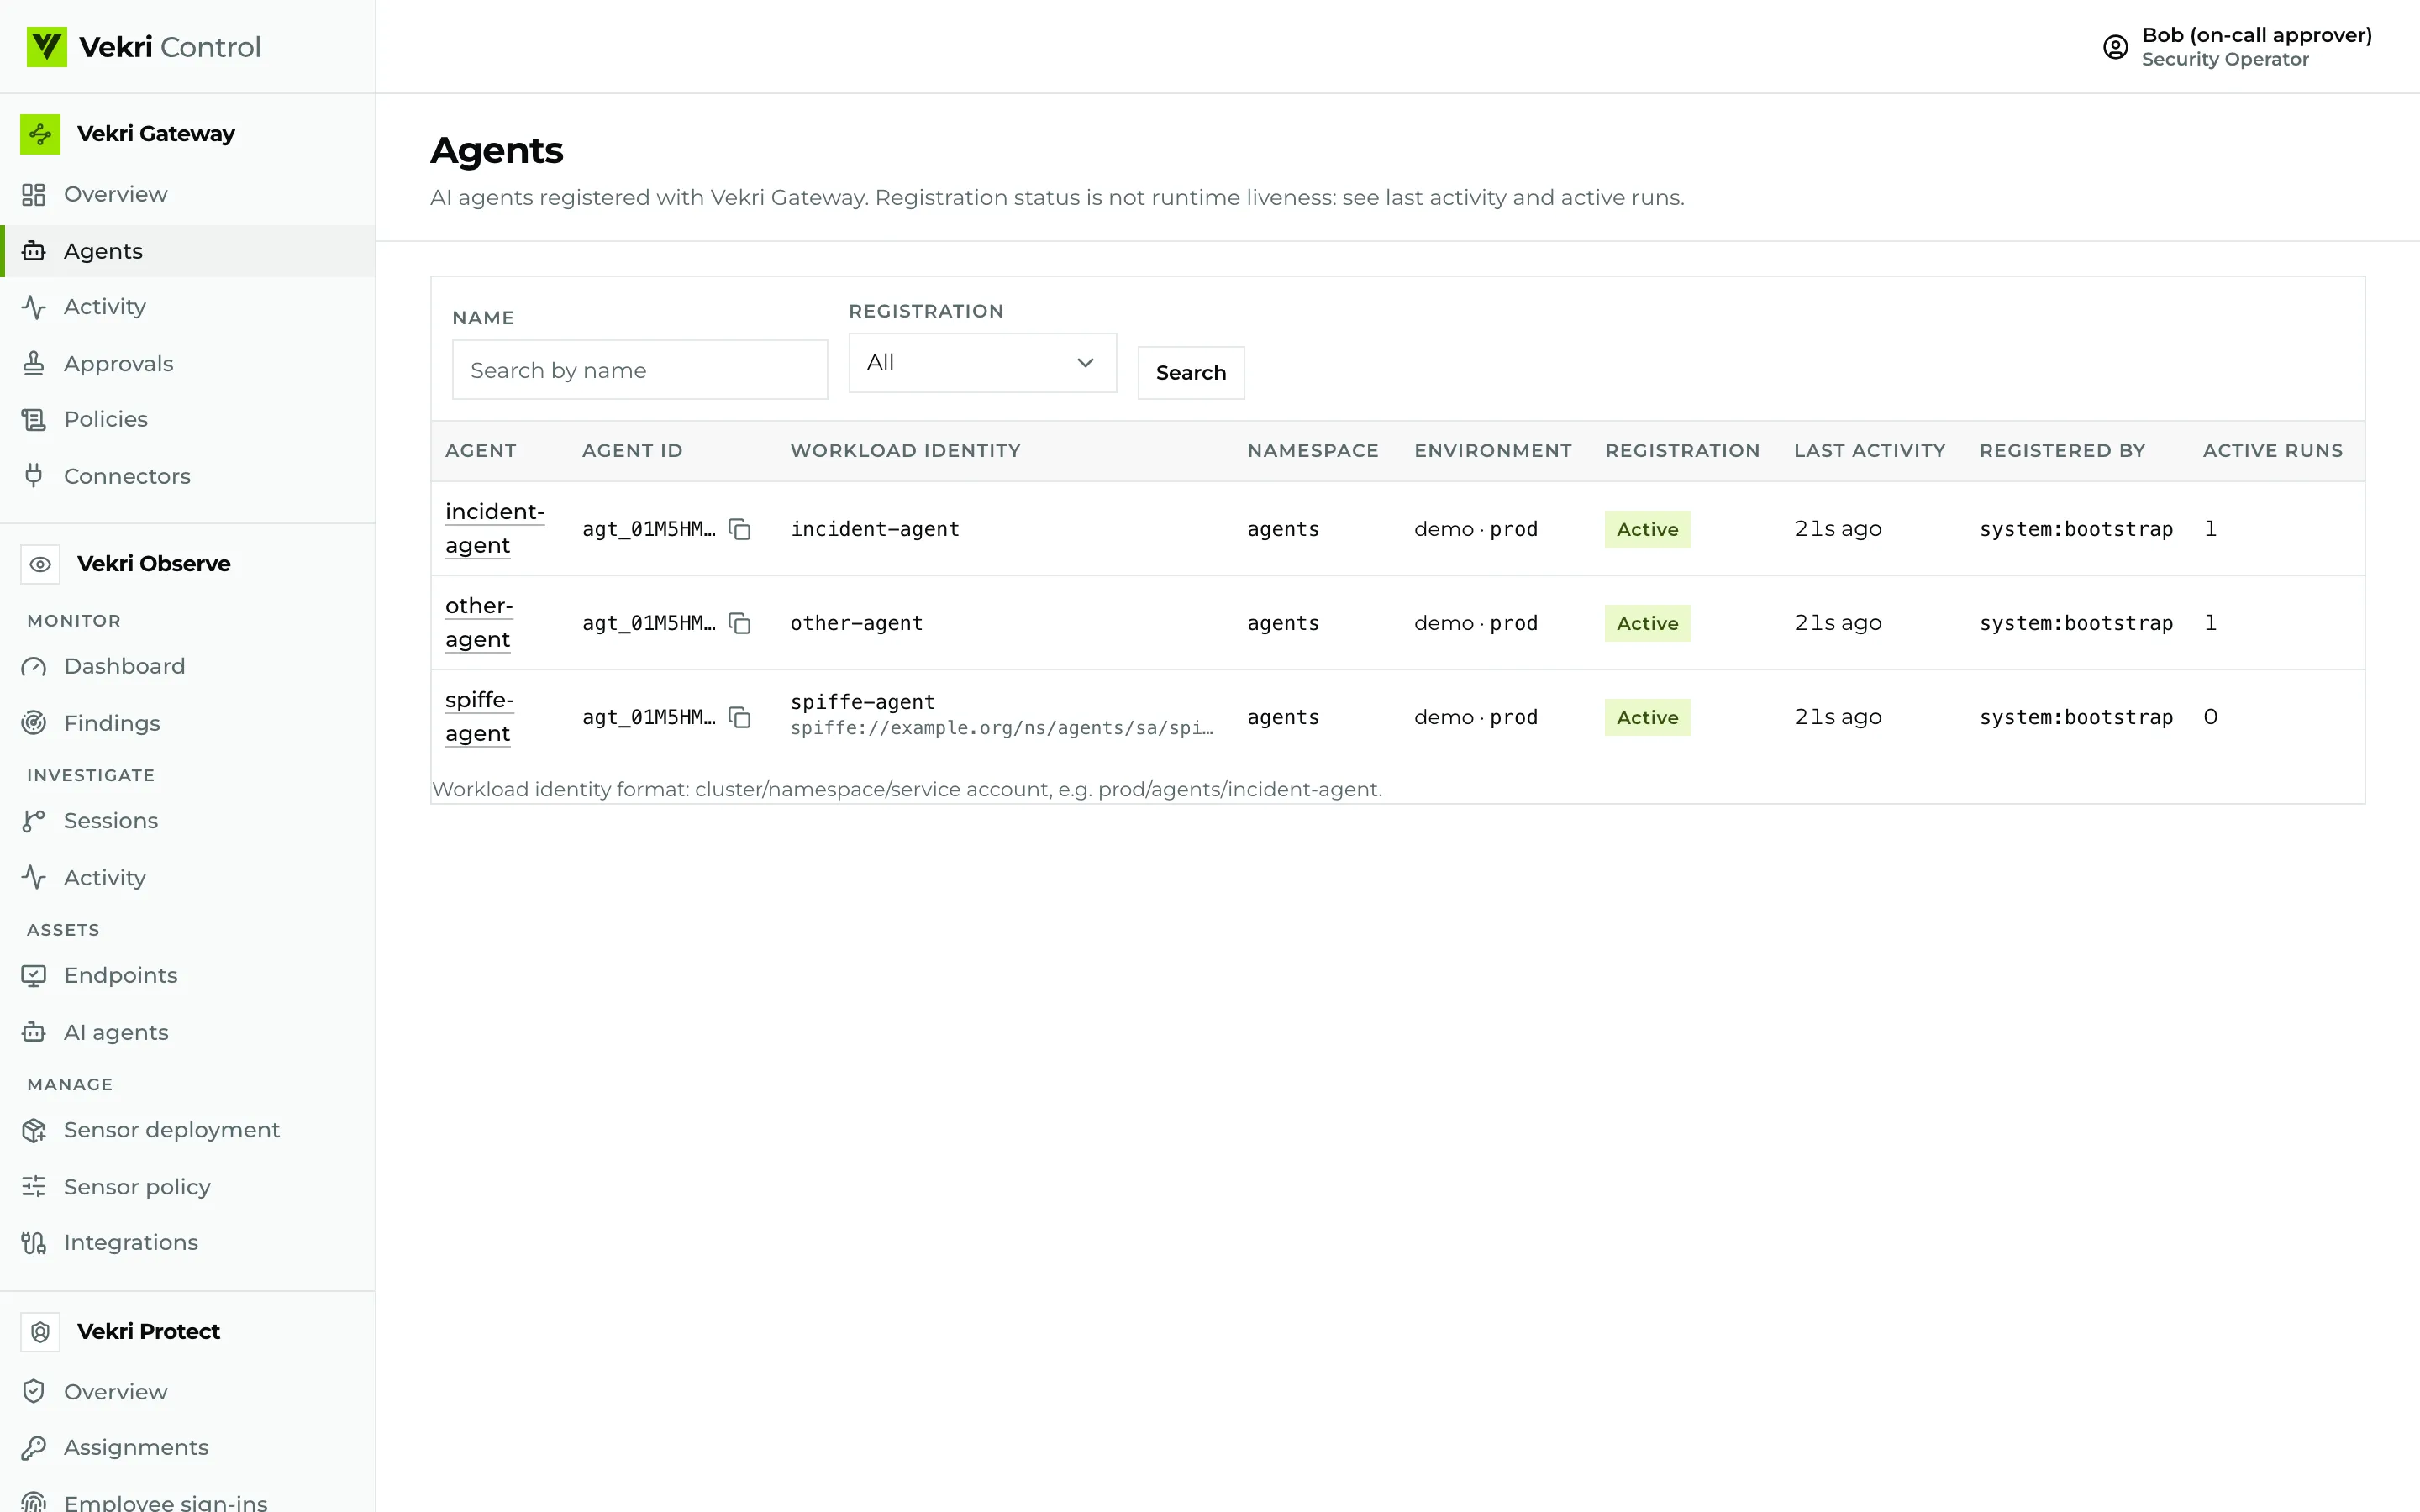
Vekri Control Agents page listing three registered agents with workload identity, namespace, registration status and active runs.Vekri Control Agents page listing three registered agents with workload identity, namespace, registration status and active runs.
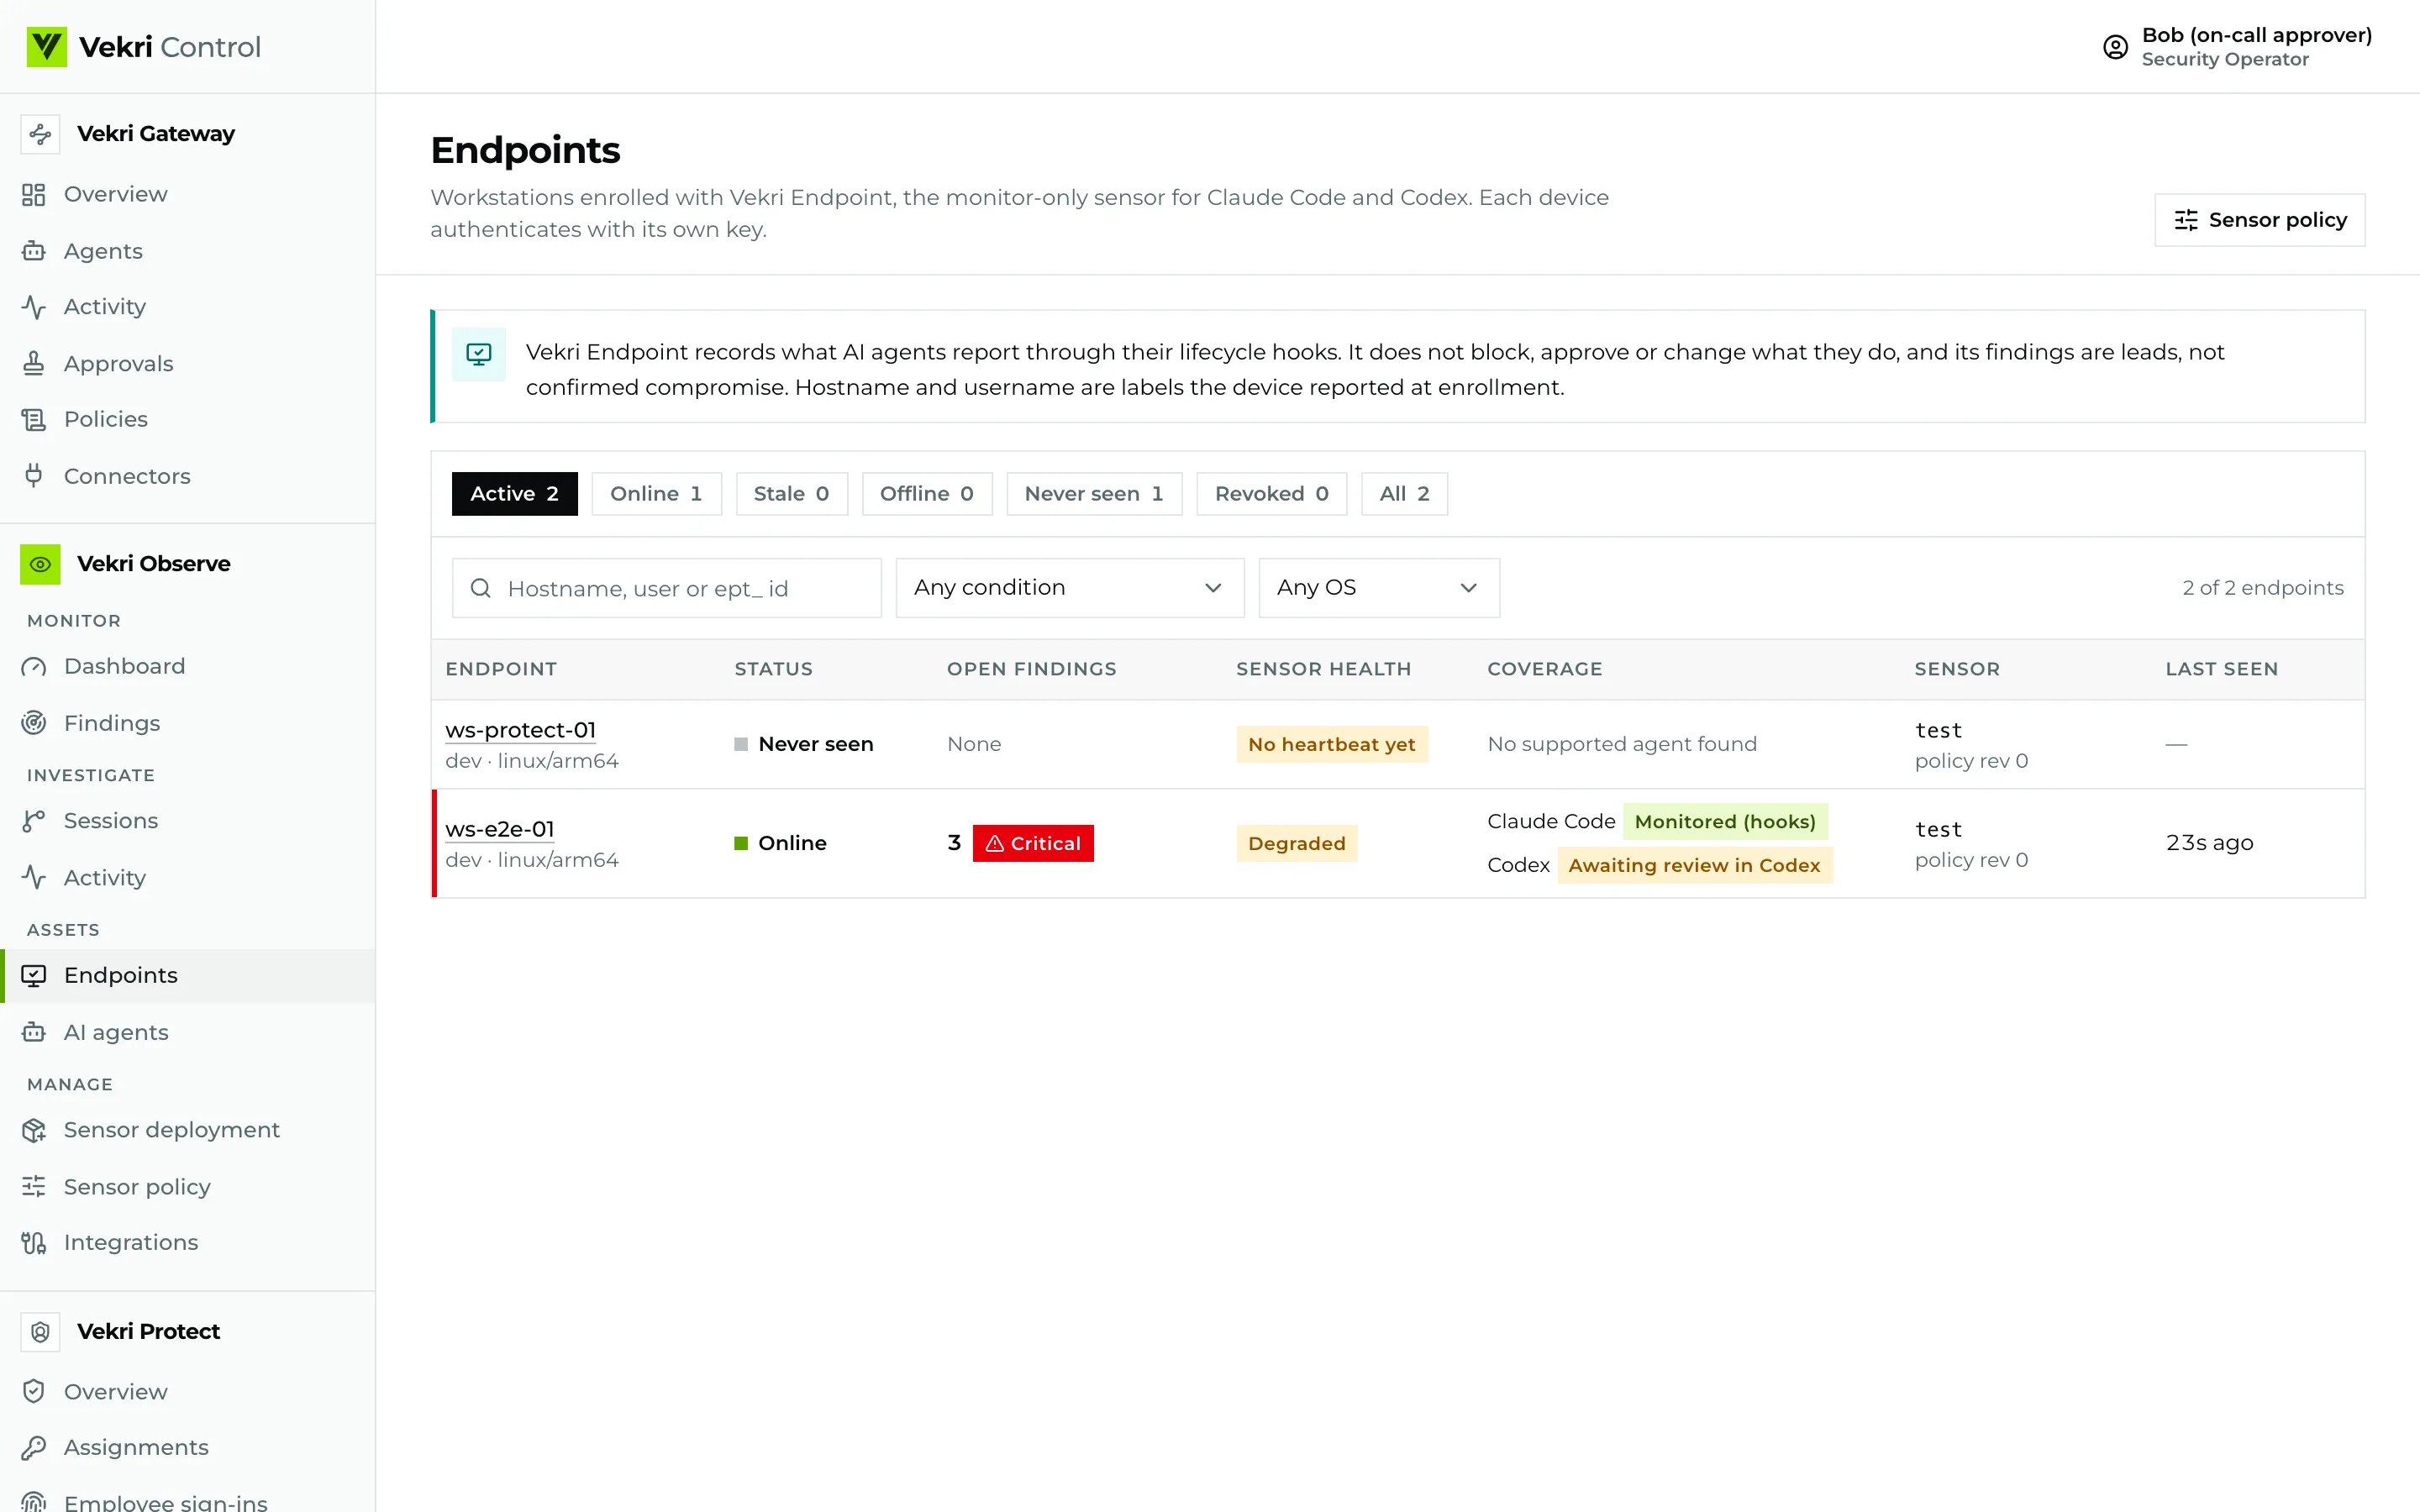
Vekri Control Endpoints page showing two workstations with status, open findings, sensor health and Claude Code and Codex coverage.Vekri Control Endpoints page showing two workstations with status, open findings, sensor health and Claude Code and Codex coverage.
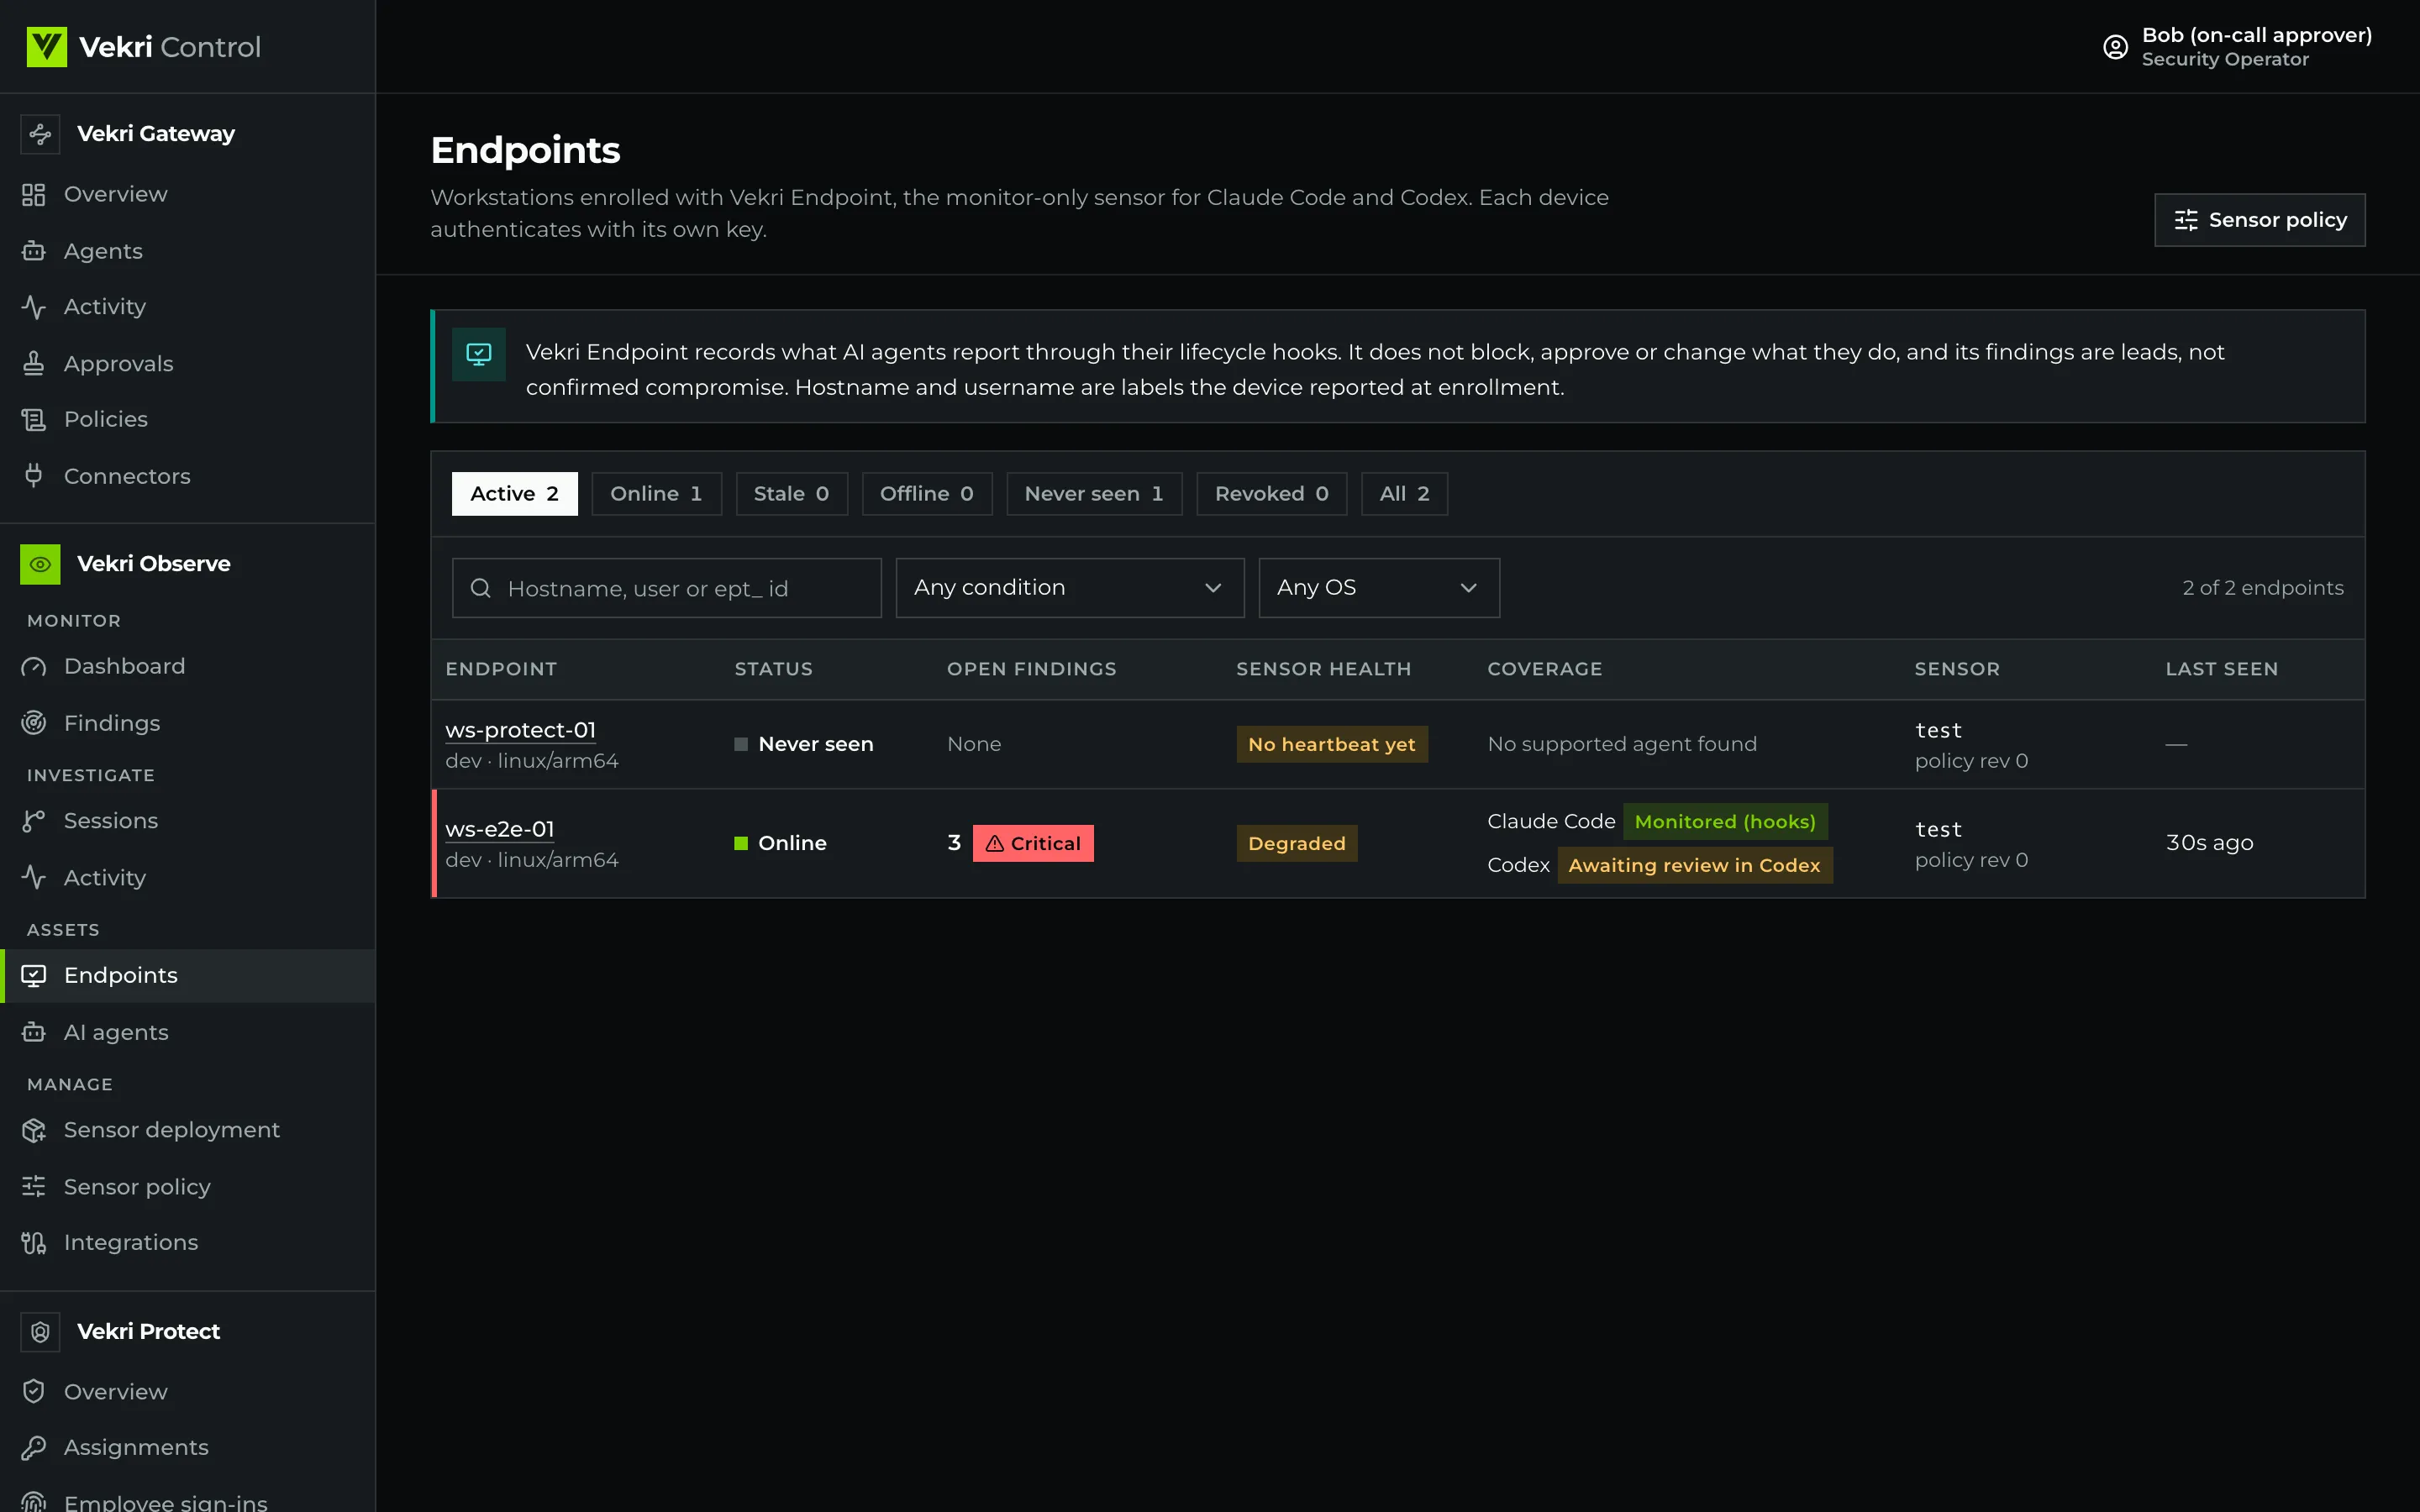
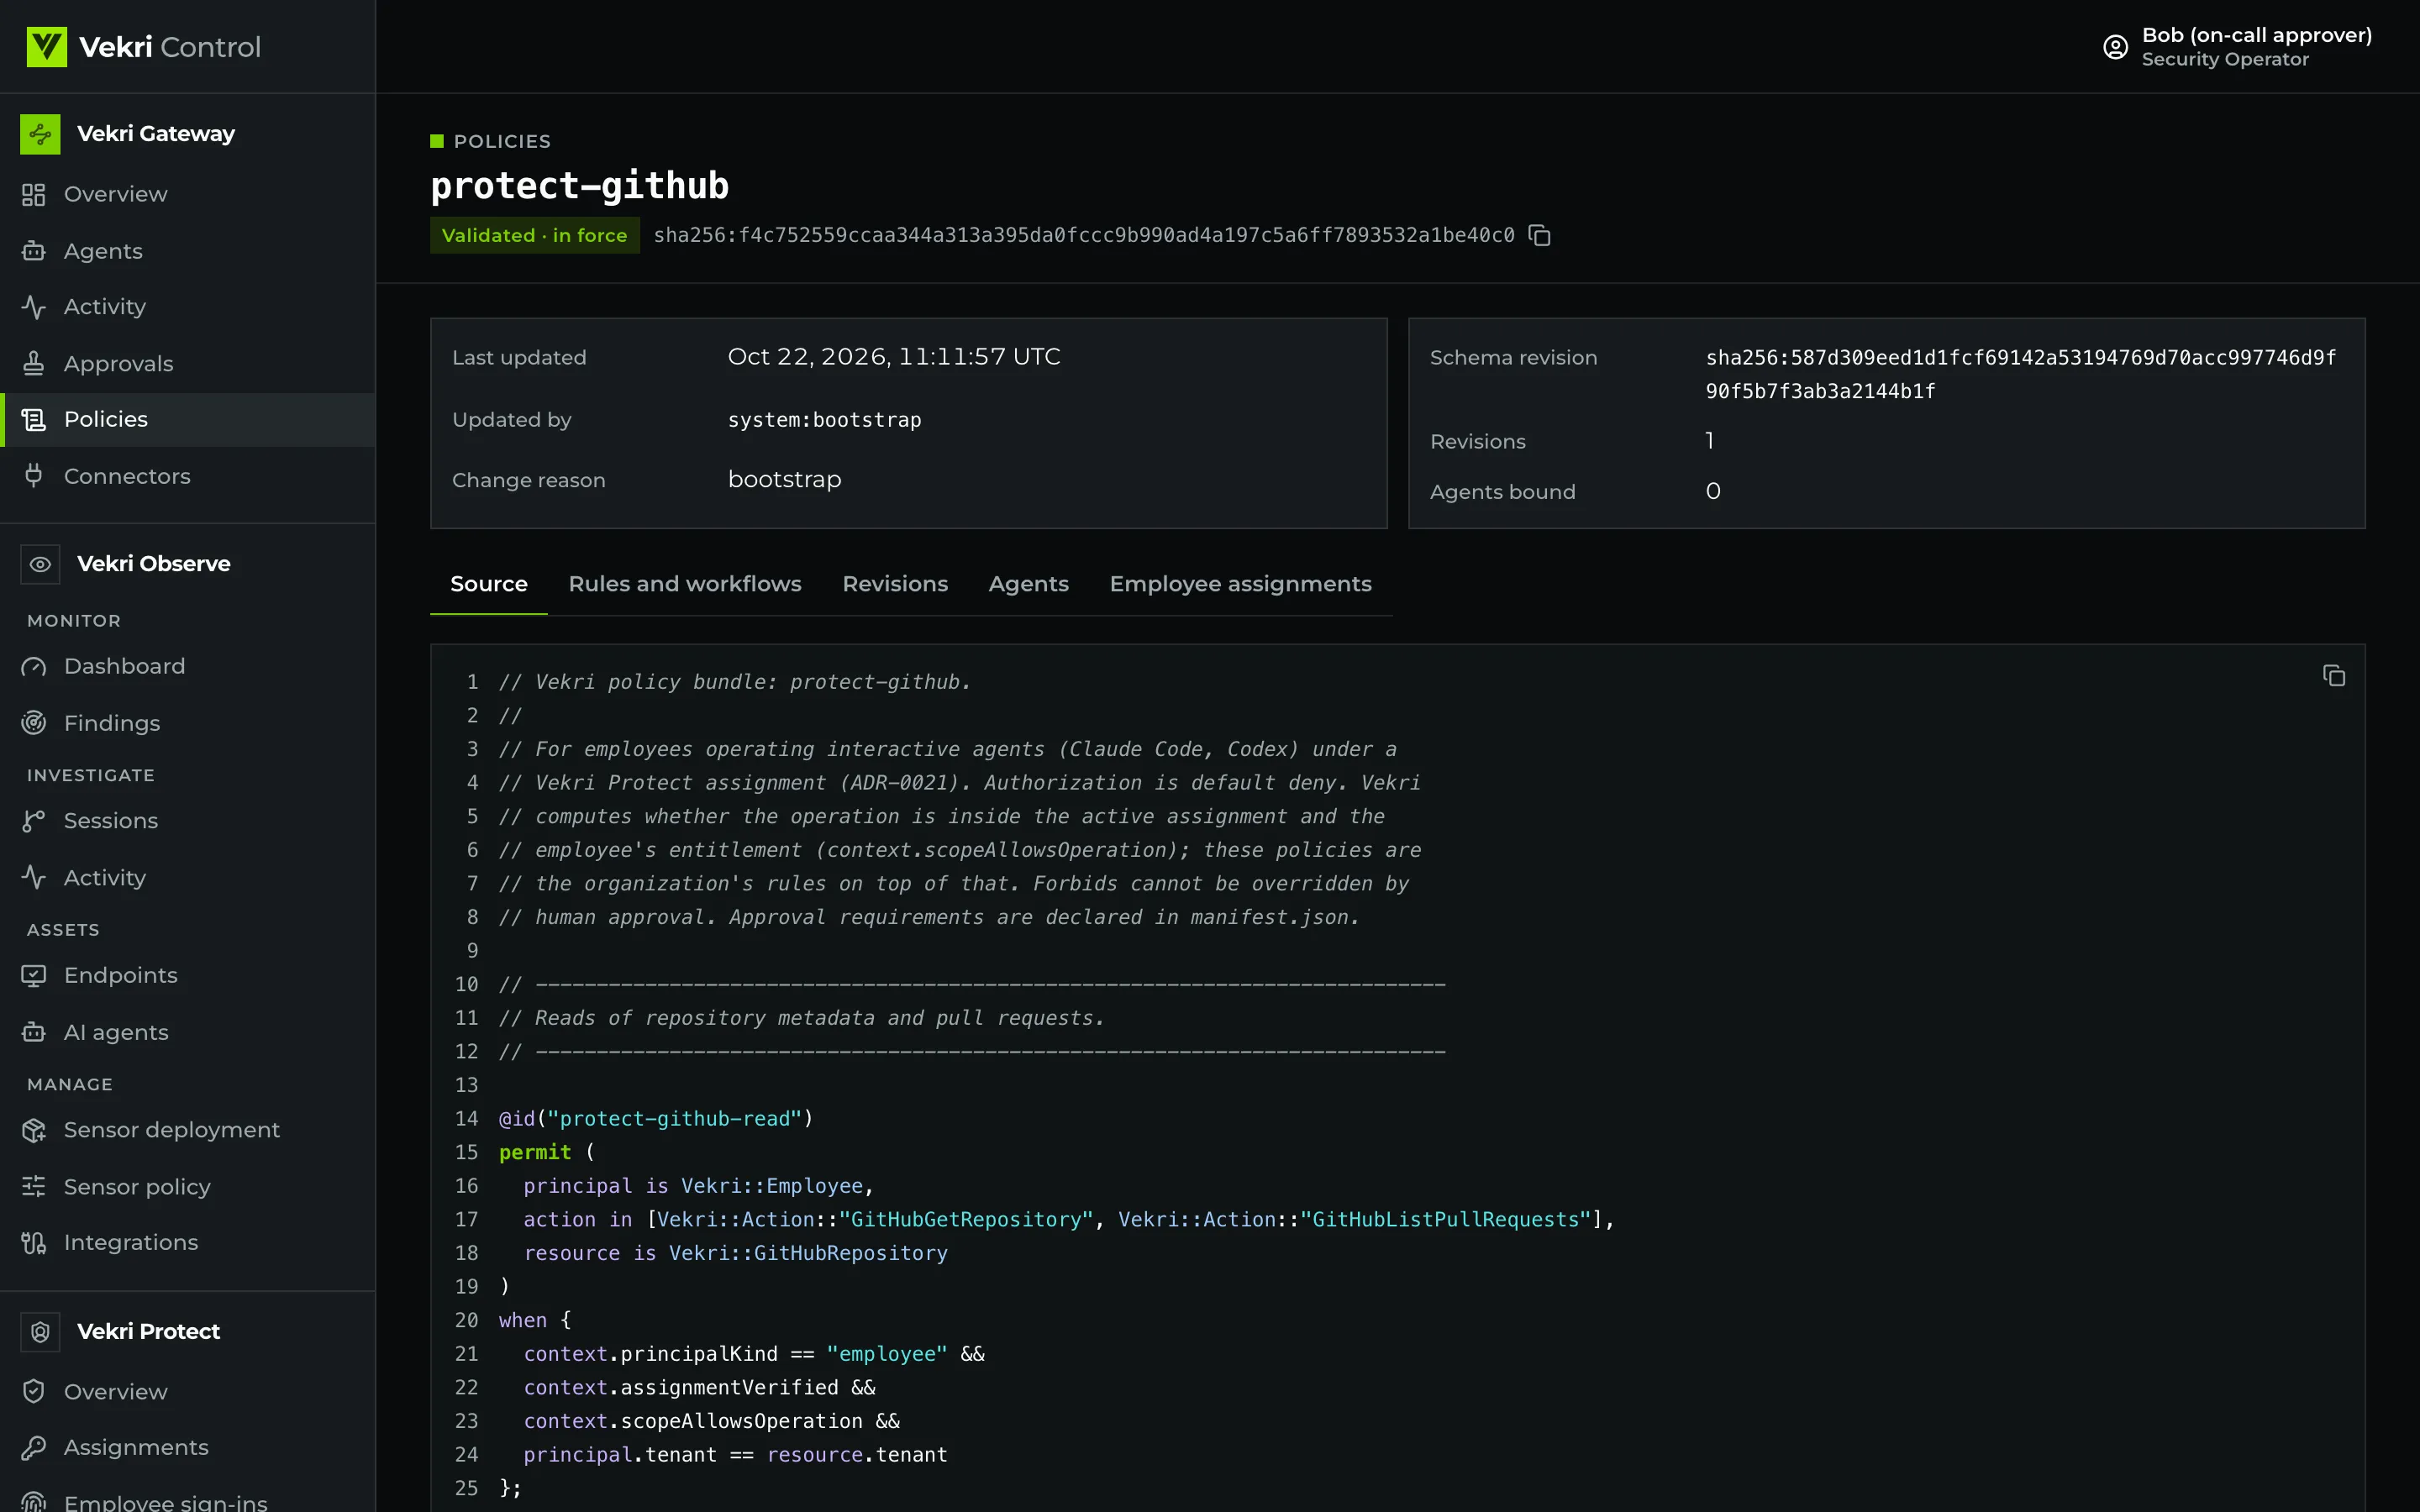
Vekri Control policy page for protect-github showing the Cedar source with a permit rule for employee reads.Vekri Control policy page for protect-github showing the Cedar source with a permit rule for employee reads.
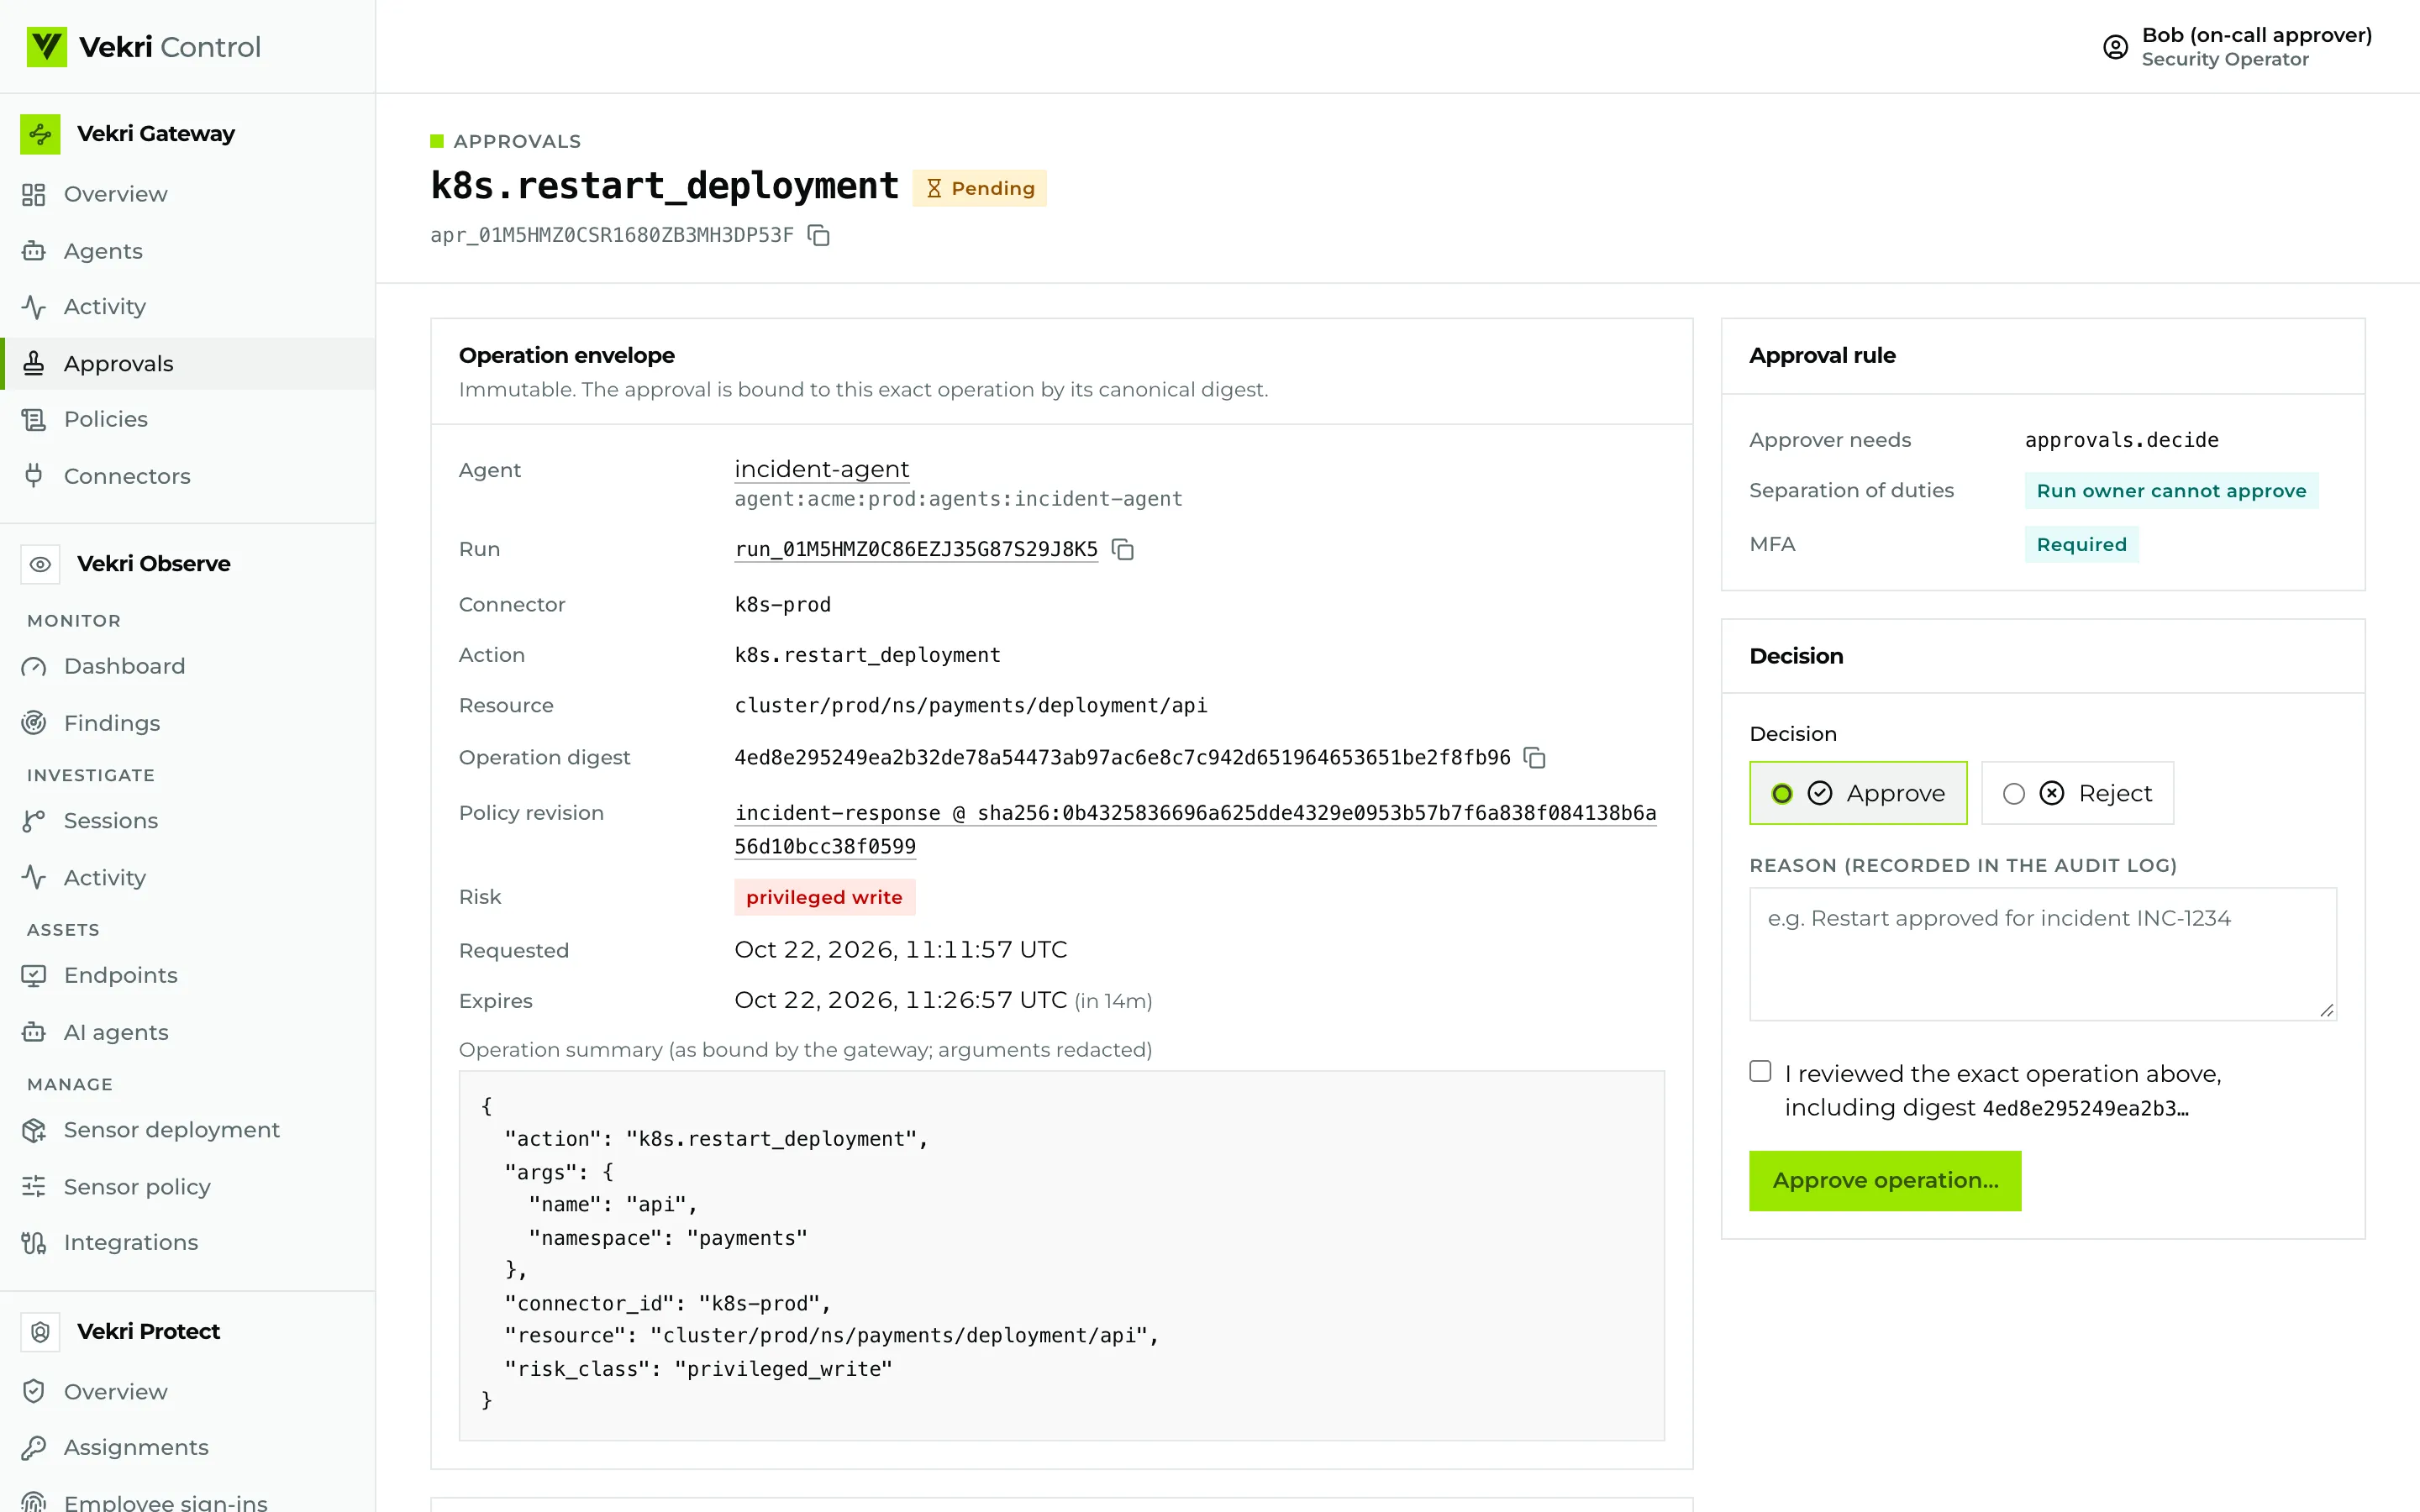
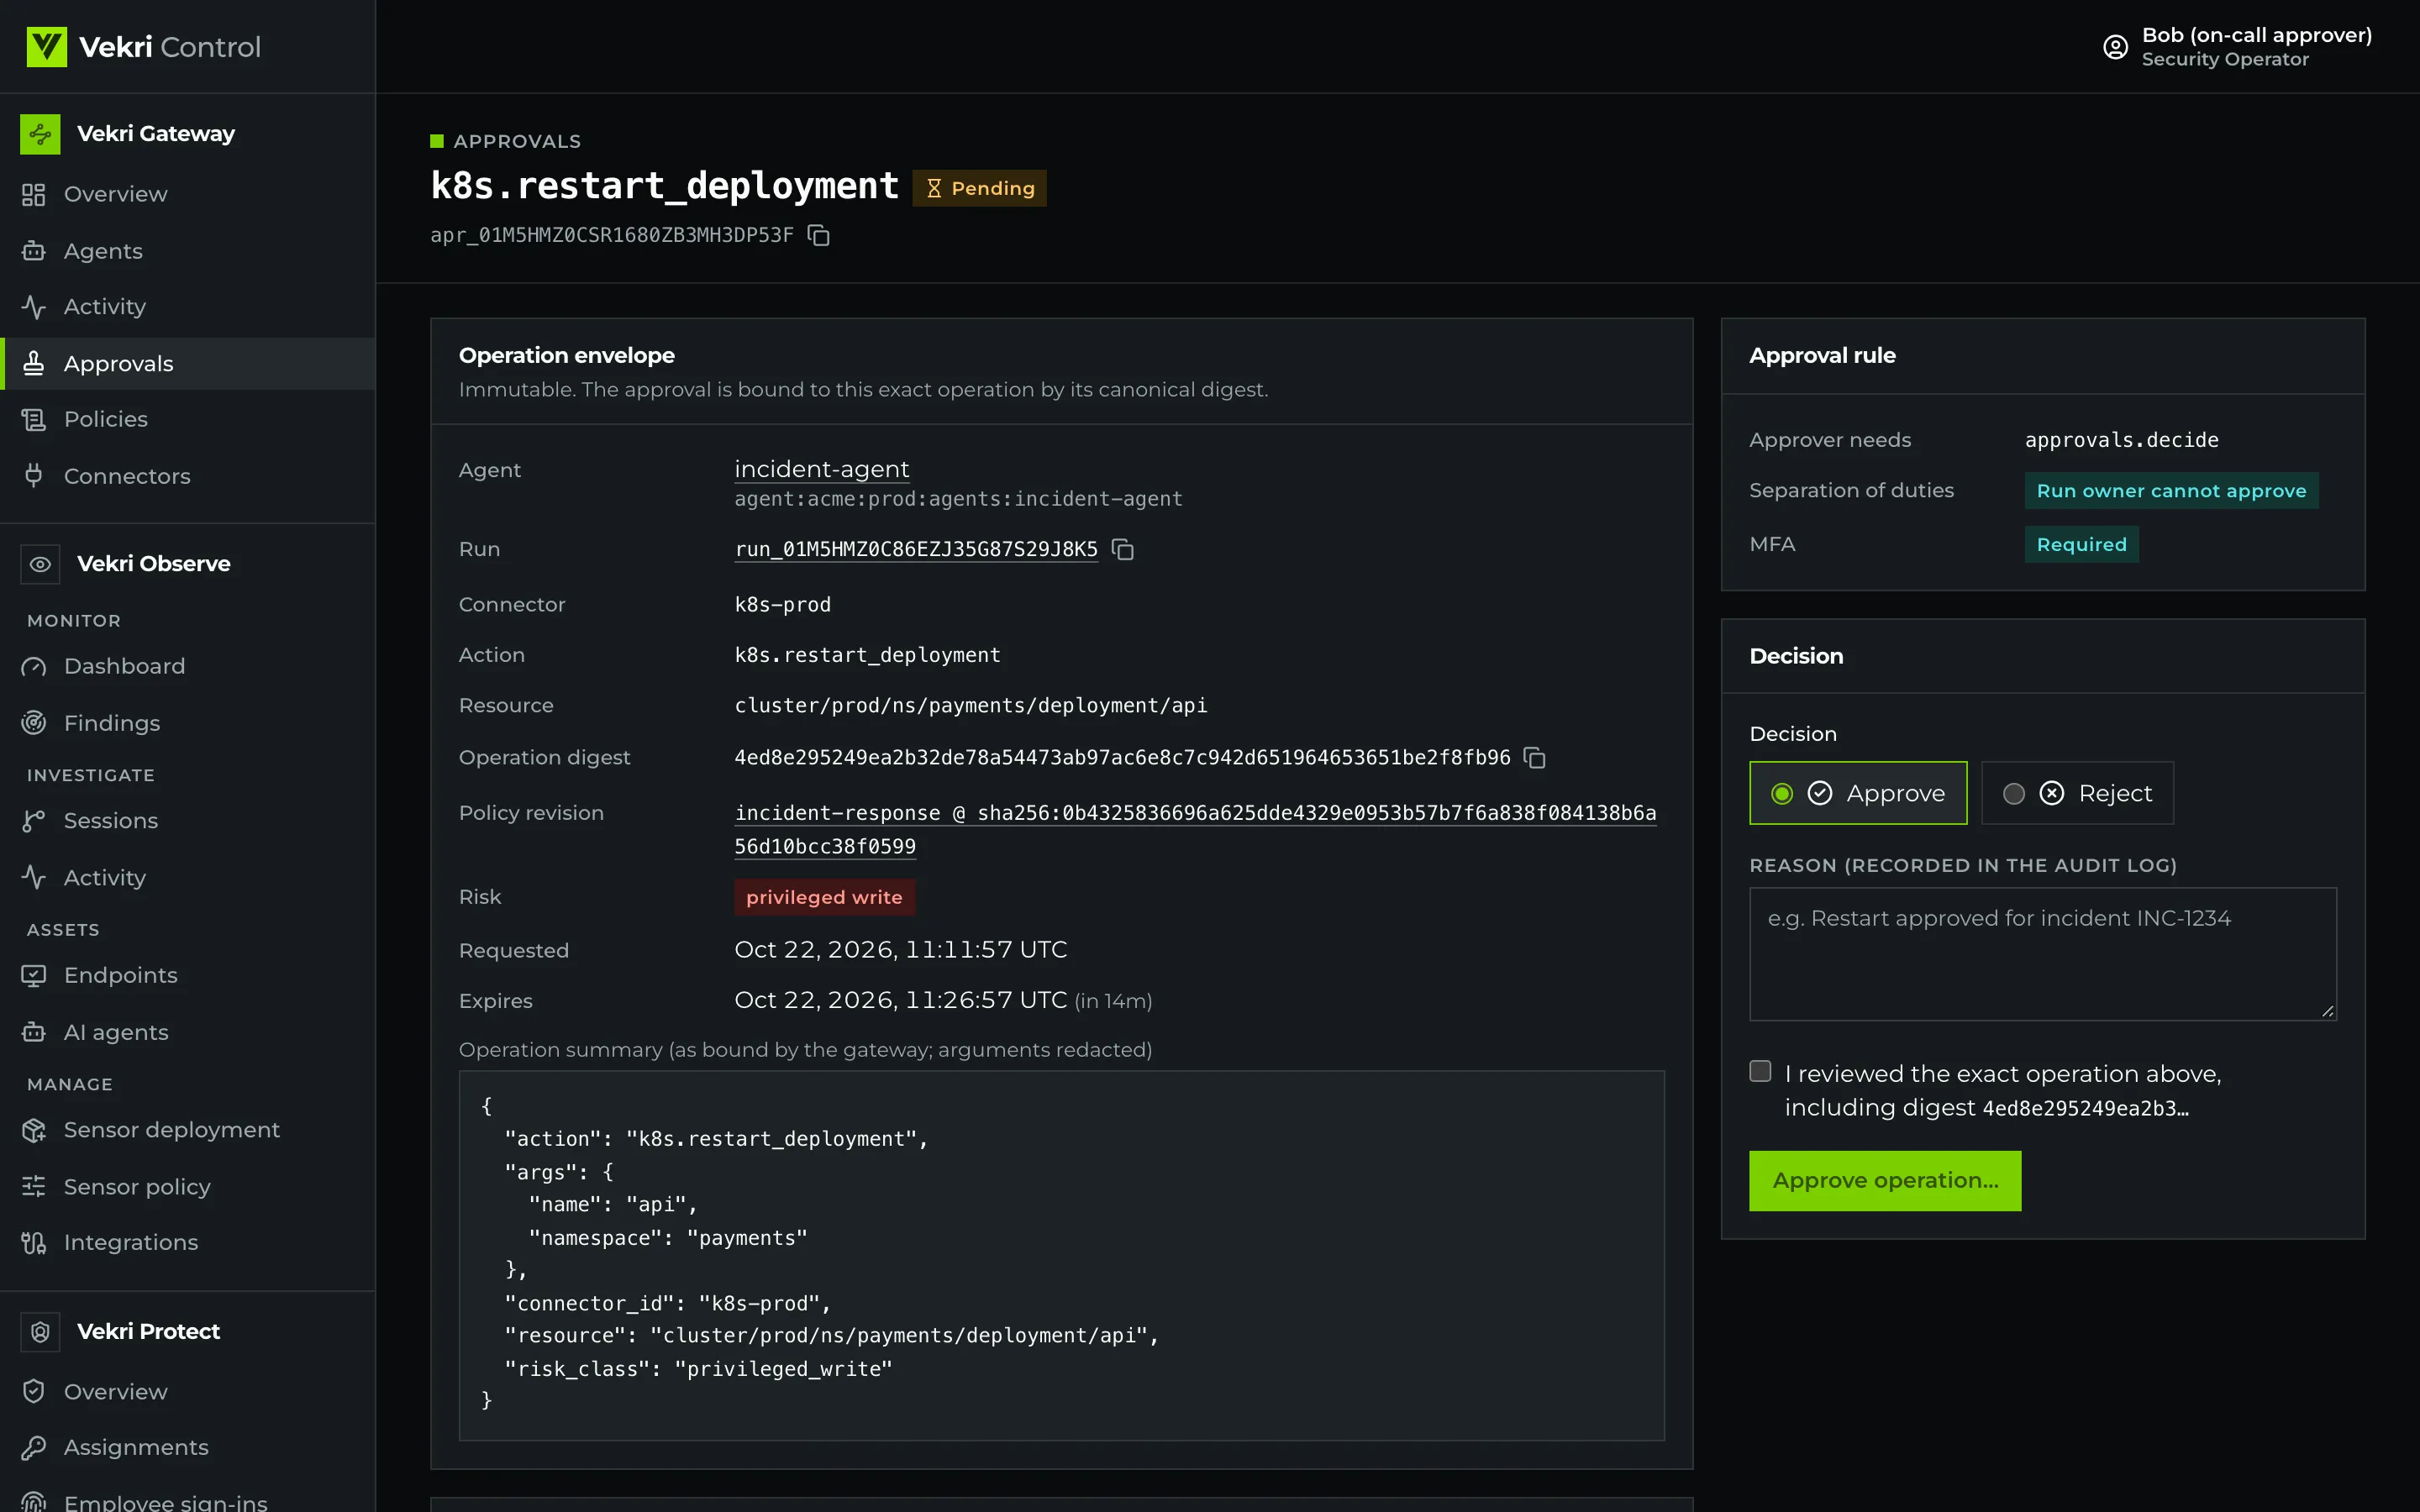
Vekri Control approval page for k8s.restart_deployment with the operation envelope, approval rule and the approve or reject form.Vekri Control approval page for k8s.restart_deployment with the operation envelope, approval rule and the approve or reject form.
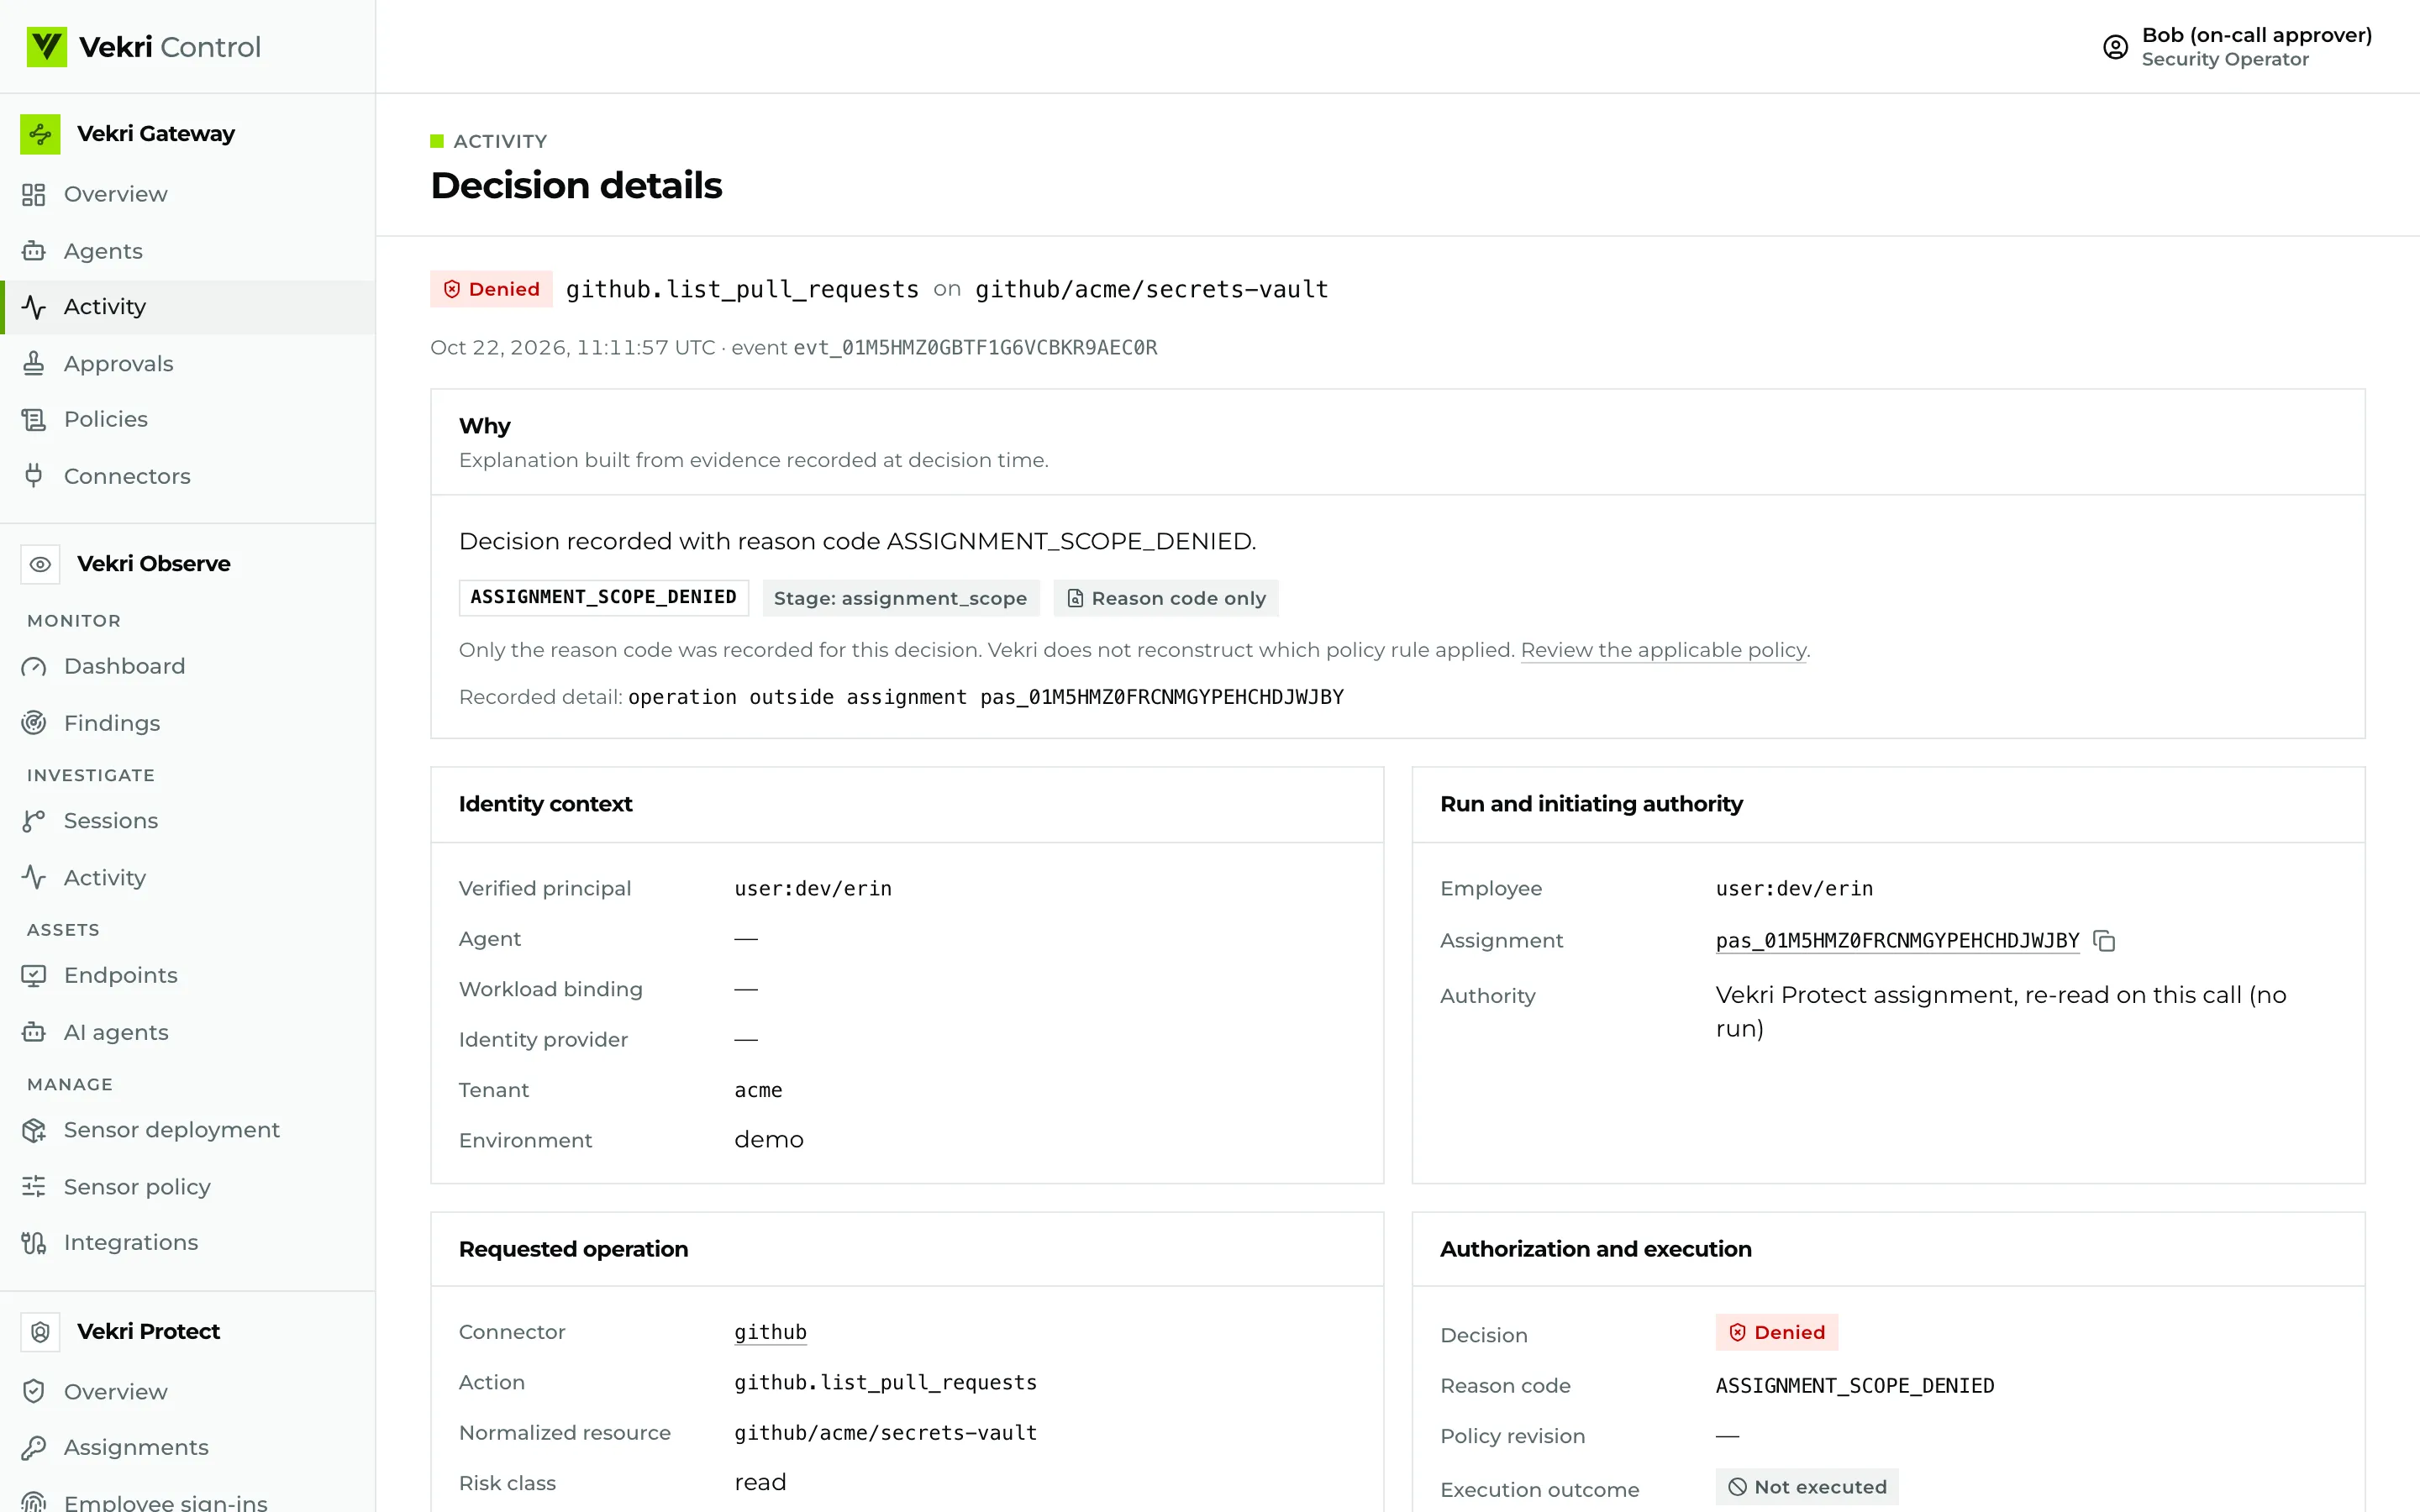
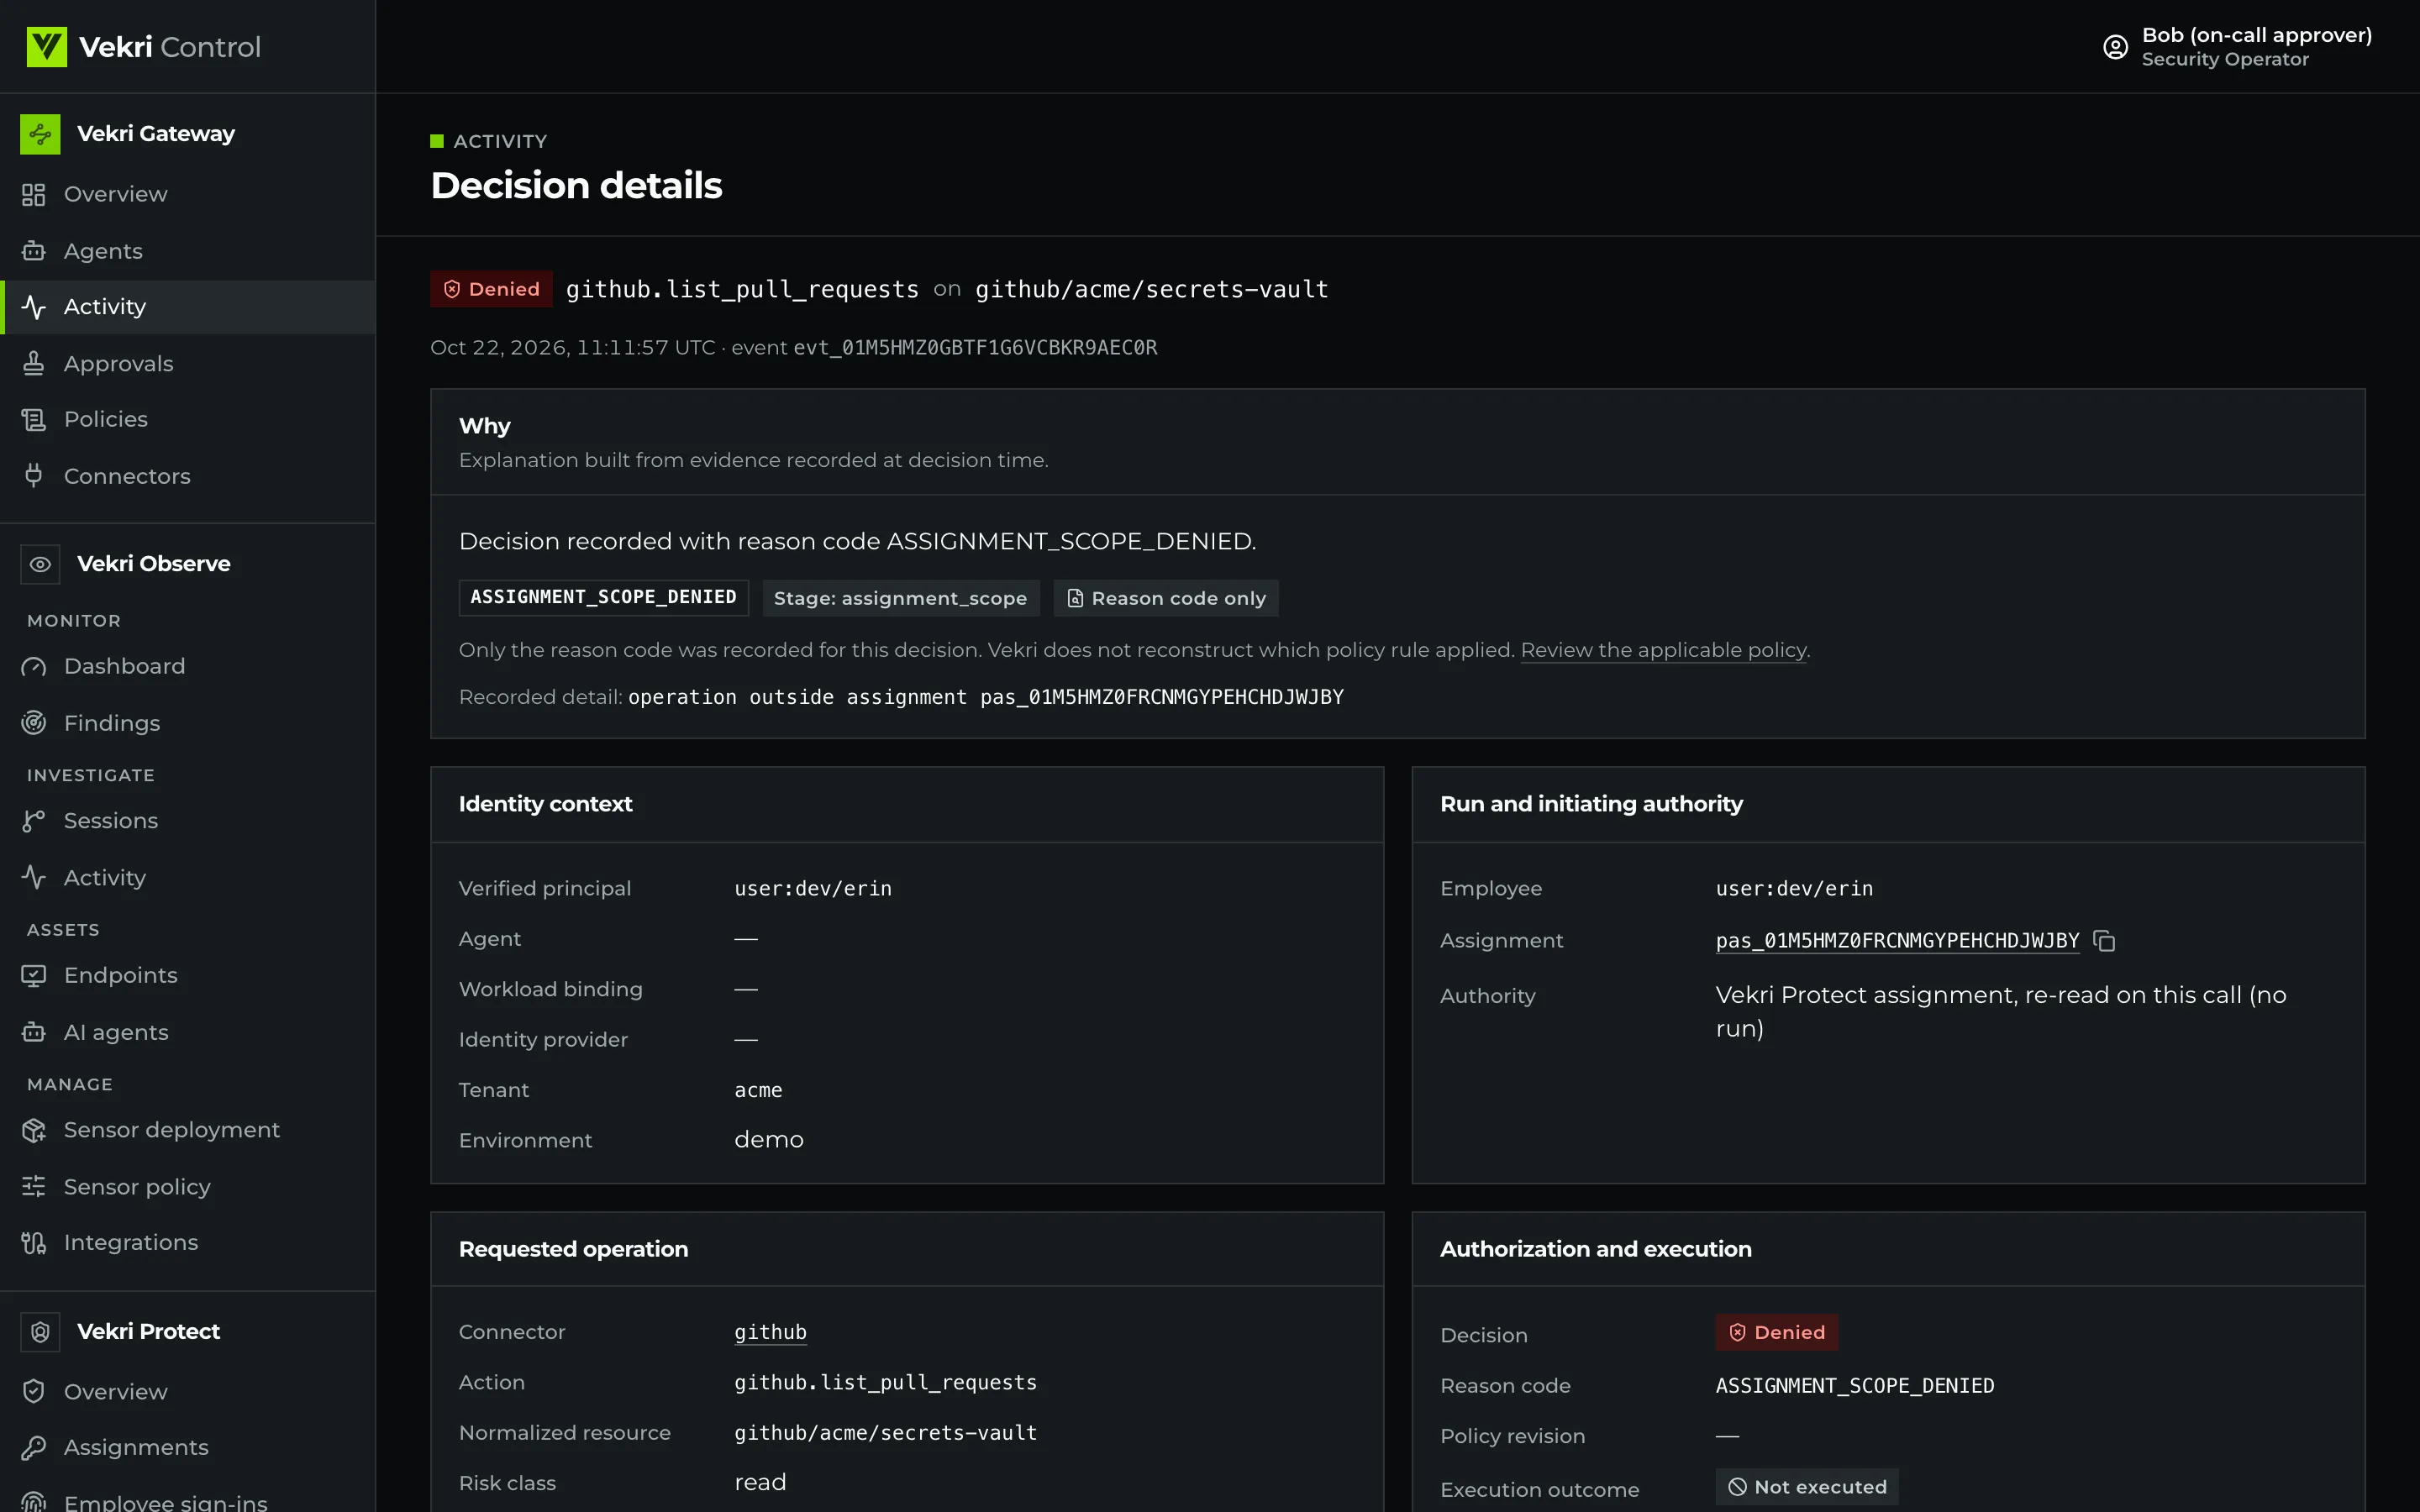
Vekri Control decision details for a denied github.list_pull_requests call, explaining the ASSIGNMENT_SCOPE_DENIED reason with identity and assignment context.Vekri Control decision details for a denied github.list_pull_requests call, explaining the ASSIGNMENT_SCOPE_DENIED reason with identity and assignment context.

What happens

Capabilities

What Vekri Control does.

Each item is in the current release and verified by tests in the product repository, with its limits beside it.
  • AI Applications inventory

    Every AI application and MCP server found across your organization, with approval status, an explainable risk score, owner, employees, first and last seen, and coverage taken from evidence.

    Vekri Control

    Limit: Approval status is enforced only where Vekri has a control point (the local MCP gateway); elsewhere it is recorded.

  • Employees, named or pseudonymous

    AI usage per verified employee, with no productivity score or ranking. Without permission, or if the organization chooses, people are shown as stable pseudonyms.

    Vekri Control

  • Sensitive-data detection management

    Twenty-one categories with an honest detector status, enable and disable with a reason, custom categories (exact values stored only as salted hashes), sample testing that stores nothing, revisions and rollback.

    Vekri Control

  • Prompt-injection settings and Test Detection

    Configure prompt-injection protection per surface, see the categories and rules, and test sample content against the detector and a draft policy without storing anything.

    Vekri Control

  • Policy simulation

    Simulate a Cedar decision, a local MCP profile or an AI usage policy without executing anything, and preview a draft policy's impact on recorded activity.

    Vekri Control

  • Connector catalog

    Lists every connector type with its maturity, how it authenticates, the permissions it needs, and each operation's risk, approval, retry and timeout.

    Vekri Control

  • Approval decisions

    See the exact operation, who asked and under which run or assignment, then approve or reject with a reason, with separation of duties.

    Vekri Control

  • Administrative roles

    Organization roles from org-owner to viewer, mapped from directory groups by their stable ids; every route checks its permission on the server, and no one can grant a role, or join a group carrying it, without holding its permissions.

    Vekri Control

  • Privacy and retention settings

    Choose whether names are shown by role or never, the minimum group size for breakdowns, and how long usage is kept.

    Vekri Control

Scope

What it does not claim.

Security tools earn trust by being exact about their limits.
  • Configuration such as connectors and deployment settings is managed through Helm values, not the console.

Contact Sales

See Vekri with your own AI applications, agents and systems.

Talk to us about the AI your organization uses, the systems agents reach and how you deploy: in Vekri's cloud, or inside your own Kubernetes cluster.